UK businesses should treat sovereign cloud as a supplier-risk decision
Sovereign cloud should address a defined business risk. UK buyers should test supplier access, dependencies, recovery and exit, then compare the full operating cost before committing to a move.
UK small and mid-sized businesses should assess sovereign cloud through supplier risk, with compliance requirements setting the boundaries of the decision. Our view is that buyers should demand evidence about access, operational dependencies, recovery and exit before paying for a sovereignty promise. Oracle describes sovereignty as a spectrum, which makes a workload-specific assessment more useful than a yes-or-no procurement checkbox.
Start with the business dependency
CTC’s editorial position is that sovereignty should earn its place in a purchasing decision through an identifiable risk reduction. A finance director should be able to explain what the additional spending buys. An IT manager should be able to demonstrate the control that delivers it.
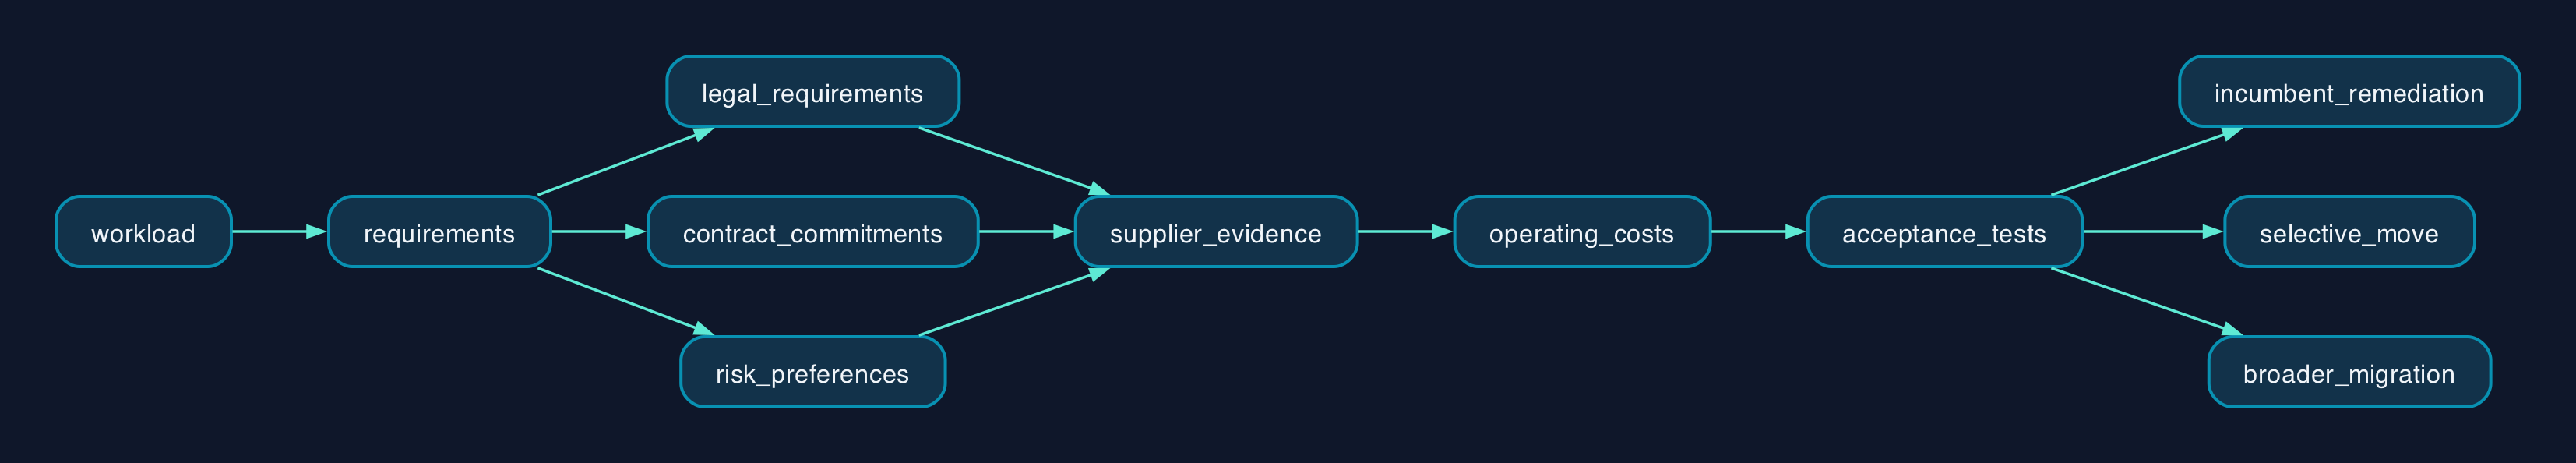
Start with a particular workload. Record who needs it, the information it holds, the interruption the business could tolerate and any location or access commitments already made to customers. Then identify the supplier decisions that could put those requirements at risk.
Consider a hypothetical UK engineering business assessing a cloud service for commercially sensitive design files. Its review should examine administrator access, subcontractors, recovery arrangements and export capability. If a customer contract requires UK-only processing, put that requirement into the acceptance criteria. Do not silently extend it to every application the business uses.
For a small IT team, the useful outcome is a short list of dependencies with named owners. A sovereignty assessment that produces a lengthy questionnaire but leaves nobody responsible for testing recovery has missed the purchasing decision.
Separate legal requirements from supplier promises
The supplier material cited here does not establish a universal requirement for UK businesses to buy UK-owned cloud, or prove that a particular ownership structure eliminates every foreign-access risk. It is insufficient evidence for either conclusion.
Keep three records separate. The first should identify applicable legal requirements, checked against authoritative sources and appropriate advice. The second should contain customer and supplier contractual commitments. The third should state the business’s own risk preferences, including any preference for domestic operations.
This is not legal advice; consult your legal counsel.
That separation improves procurement. A board preference for UK control deserves an explicit discussion about cost and scope. A binding customer requirement needs demonstrable fulfilment. Neither should disappear inside a supplier’s generic compliance statement.
The provider’s UK sovereign cloud page makes broad promises about UK hosting, operations and legal authority. Ask which commitments appear in the service agreement, which subcontractors they cover and what happens if the operating model changes. Treat the sales page as the beginning of due diligence.
Map who can act when something goes wrong
The operational assessment should trace the application, its data, backups, administrative access and supporting services. The vendor’s account of sovereignty capabilities explicitly extends the discussion beyond databases to processing, networks, backups, disaster recovery and personnel.
Use that scope to request evidence. The following is a proposed responsibility map, not a description of any supplier’s contracted service.
| Decision area | Evidence to request | Proposed customer owner |
| --- | --- | --- |
| Data location | A service-specific record covering production data, backups, logs and support attachments, with exceptions identified | IT lead |
| Administrative access | Who can grant privileged access, where administrators work, approval controls and accessible audit records | Security or IT lead |
| Supplier dependencies | Contracting entity, relevant subcontractors, critical technology dependencies and change-notification terms | Procurement lead |
| Recovery | Agreed recovery objectives, test results and dependencies needed to restore service | Business service owner |
| Exit | Export formats, assistance scope, charges, deletion arrangements and a demonstrated migration route | IT and procurement leads |
For a smaller business, one person may hold several roles. The requirement is a named decision-maker with access to the evidence.
Ask the provider to walk through a support incident involving sensitive information. Then ask it to walk through a regional outage and a contract termination. These scenarios give procurement and technical staff a common way to examine the promised controls.
Put the full operating cost into the decision
The evidence available for this article does not establish comparable prices or a defensible sovereignty premium. A numerical price comparison would therefore mislead.
Request quotations against the same workload, support hours, recovery objectives and contract period. Require the currency, VAT treatment, billing commitment, minimum spend and exclusions to be explicit. Compare the existing arrangement with the proposed replacement over the same evaluation period.
Include the following costs in the assessment.
- Transition work including discovery, application changes, data migration, testing and parallel operation.
- Ongoing operation including infrastructure, connectivity, support, monitoring, administration and staff training.
- Assurance work including evidence collection, access reviews and recovery exercises.
- Exit work including data export, replacement infrastructure, migration assistance and contract overlap.
The provider’s design documentation provides a concrete reason to investigate transition effort. It specifies separate accounts and independent identity and billing systems for the service. Buyers should therefore ask their implementation team to scope account administration, access configuration and billing integration before assuming that familiar technology means a simple move.
Leave unknown costs visible. An unpriced migration is an unresolved input, not a saving.
Choose the arrangement that addresses the identified risk
Keeping an existing service should remain a serious option. Where the assessment identifies a permissions problem, an undocumented recovery dependency or weak contractual reporting, first establish whether the incumbent can remedy it. Set a completion condition and ask for evidence.
A UK-focused service merits consideration when the workload has a substantiated UK location or operational-control requirement. The published offering is one candidate for that assessment, but the material cited here does not establish comparative support quality, application compatibility or total cost.
An EU-focused service requires a different geographical assessment. The provider describes its sovereign cloud as physically and logically separate infrastructure within the EU, beginning in Germany. A buyer with a UK-only requirement should recognise that distinction before assessing its other controls.
A selective move is also worth evaluating. In the hypothetical engineering business, the sensitive design repository could warrant a different arrangement from less sensitive applications. Before splitting the estate, price the additional access management, monitoring, support coordination and recovery testing.
Our recommendation is to choose the smallest operational change that satisfies the substantiated requirement and passes the agreed tests. A broader migration needs a broader business case.
Editorial analysis
The strongest counterargument is that sovereignty belongs with compliance because some purchasing requirements are mandatory. That is a fair starting point. A service that cannot meet an applicable requirement should fail that stage of selection.
The remaining decision still needs supplier-risk analysis. After an offering meets the entry criteria, the buyer must judge whether its team can operate it, recover the business service and leave on acceptable terms.
A sovereignty commitment should therefore have an owner, supporting evidence and a review trigger. Set triggers for material changes in ownership, subcontractors, support arrangements or service scope. Agree what would prompt remediation and what would prompt an exit review.
For the next renewal, choose one important workload and require a joint review by its business owner, IT lead and procurement owner. Finish with documented acceptance criteria, unresolved questions and an accountable decision. That is a more useful result than another tick beside “sovereign”.
FAQ
Does choosing sovereign cloud make our business compliant?
Do not treat the label as evidence that your particular obligations have been met. The vendor describes security and privacy as shared responsibilities between provider and customer. Assess the actual service, configuration and commitments against your requirements.
Is this sovereign cloud a UK hosting option?
The cited opening announcement places its first region in Brandenburg, Germany, and describes infrastructure located within the EU. That does not establish UK residency for a proposed deployment. Specify the required country and verify the exact service location.
Should a small business move everything to one sovereign provider?
Our recommendation is to assess important workloads individually before choosing the scope of a move. Compare a selective migration with the administrative cost of running multiple environments. Require evidence that the proposed arrangement solves the identified problem before committing the whole estate.
What should we ask a supplier to demonstrate first?
Ask it to trace a representative workload through normal operation, a support incident, recovery and exit. Request evidence of access controls, dependencies, recovery results and export arrangements. Treat successful demonstrations and agreed contractual commitments as purchasing criteria.