Huntress is the only one of the three that publishes a price, $7.99 to $8.99 per endpoint per month. Arctic Wolf and Sophos MDR are both quote-only. The bigger question for a security manager with no in-house SOC is who acts during an attack and on which tier. Sophos gates full incident response and its warranty behind MDR Plus, not the entry Sophos MDR tier, while Arctic Wolf and Huntress both build response into their core offering.
Key pointers
- Get a Huntress quote first as a budget anchor. Its published range, $7.99 to $8.99 per endpoint per month, is the only figure of the three you can put in a business case before speaking to a salesperson.
- If you talk to Sophos, ask specifically about MDR Plus rather than the entry Sophos MDR tier if you want a named Incident Response Lead and a contractual SLA rather than a target.
- Ask Arctic Wolf for the exact contract length on the table. Third-party pricing research describes its deals as typically multi-year, which limits how easily you can leave if the service underperforms.
- Ask each supplier how they actually respond, not just how fast. Huntress's Managed Response and Sophos's "Authorize" mode both let the SOC act on your endpoints without waiting for a click; decide whether your team is comfortable with that or wants sign-off first.
- Get every quote confirmed in GBP with VAT treatment spelled out in writing. None of the three publish a UK sterling price list.
- If a worst-case ransomware payout matters to your board, compare Arctic Wolf's published $3 million Security Operations Warranty against Sophos's MDR Plus breach-protection warranty, which caps reimbursement at $1,000,000 a year, $1,000 per breached endpoint, and $100,000 for a ransomware payment itself. No comparable financial warranty appears on the Huntress pages reviewed for this article.
- Decide whether to buy Huntress direct or through a partner. Huntress now has a UK-registered company (Huntress Labs UK Ltd), but it still describes most sales as running through an MSP or reseller, which removes any Huntress-required minimum seat count but adds a layer of day-to-day console management that its base SOC price does not include.
What "Managed Detection and Response" Actually Buys You
All three services do the same basic job: they put a 24/7 human security operations team behind your endpoints so an IT security manager without a dedicated SOC does not have to staff one internally. The differences that matter to a UK mid-market business sit in three places: how much control the vendor's analysts have to act on your systems without asking first, how deep their support goes once an incident is confirmed, and how transparent the pricing is before you get on a sales call.
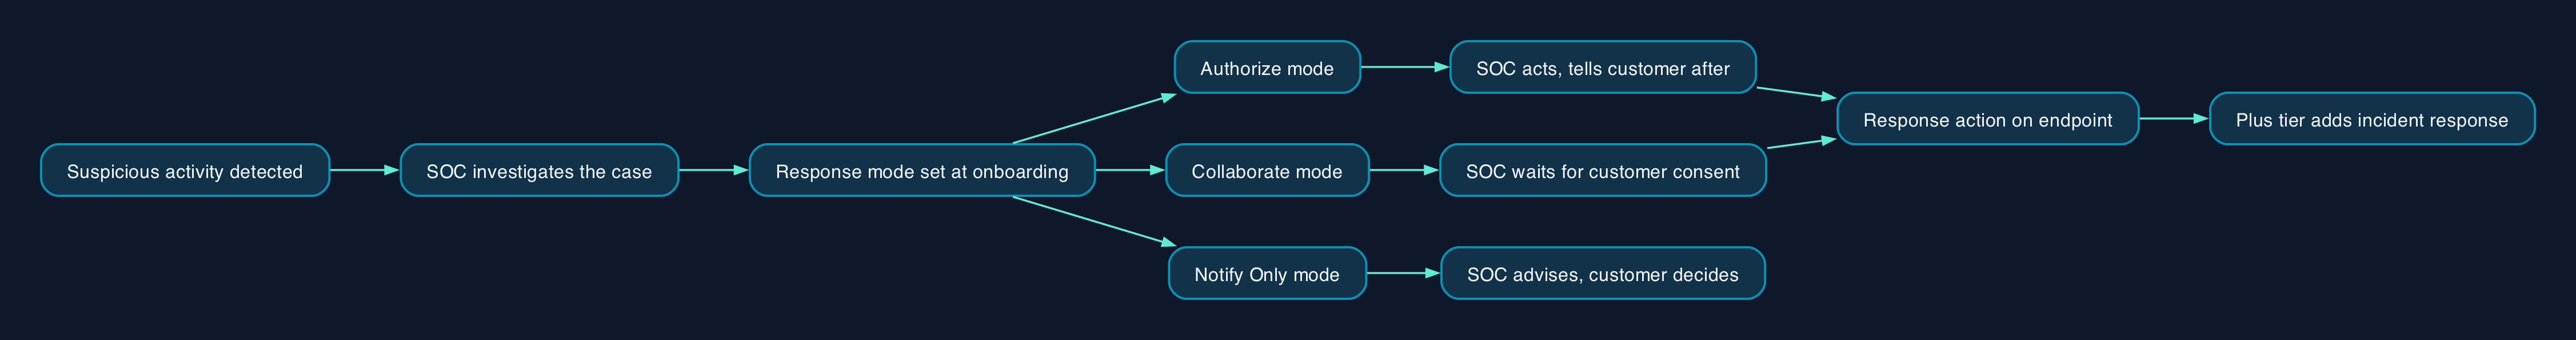
Sophos publishes the clearest public description of the mechanics, because its official Service Description spells out a "Threat Response Mode" that a customer selects at onboarding. Under "Authorize", Sophos acts independently and tells you afterwards. Under "Collaborate", Sophos investigates but needs your written consent before most response actions, other than limited steps like a remote query or evidence collection; a configurable sub-option called "Collaborate then Authorize" lets Sophos switch to acting independently if it cannot get an acknowledgement from anyone on your contact list. Under "Notify Only", Sophos investigates and advises but takes no response action at all, and Sophos's own terms warn that this "can materially delay containment and disruption actions and may increase risk" to your systems. Huntress runs a comparable idea under a different name: its Managed Response feature lets the Huntress SOC isolate hosts, kill processes, remove persistence mechanisms and lock out compromised Microsoft 365 accounts automatically the instant a threat is confirmed, and it has been switched on by default for new Huntress partners since Q4 2025. Arctic Wolf describes its equivalent as an "Agentic SOC" working with humans in the loop, delivered through what it calls the Concierge Experience, but it does not publish the same level of contractual detail on response modes that Sophos does.
How the Three Actually Price the Service
Huntress is the only vendor of the three that puts a number on its own website. Its Managed EDR product costs $7.99 per endpoint per month once you cross 100 endpoints, and $8.99 per endpoint per month at the 50 to 99 endpoint band. Huntress sells related modules separately, all at the 100-plus unit rate, with per-unit prices at the 50 to 99-unit band running between about 12% and 33% higher depending on the module:
| Huntress module | Unit | Price at 100+ units | Price at 50-99 units |
|---|---|---|---|
| Managed EDR | Per endpoint/month | $7.99 | $8.99 |
| ITDR (identity threat detection) | Per licensed identity/month | $3.60 | $4.80 |
| Managed SIEM | Per data source/month | $3.50 | $4.00 |
| Security Awareness Training | Per learner/month | $1.75 | $2.08 |
| ISPM (identity posture management) | Per licensed identity/month | $3.40 | $4.00 |
Source: Huntress pricing page. None of that is a full MDR "bundle" price; a mid-market business layering identity monitoring and SIEM on top of EDR should expect to add those unit prices together.
Assumptions. Huntress prices in US dollars and publishes no GBP list. Using the GBP/USD spot rate of roughly 1.3250 quoted on 29 September 2026, its $7.99 to $8.99 per endpoint range works out to an indicative £6.03 to £6.78 per endpoint per month, calculated as $7.99 divided by 1.3250 and $8.99 divided by 1.3250. That is a same-day currency estimate for budgeting only, not Huntress's UK price; a partner-negotiated quote in sterling will differ and should be used for any actual business case. On the same rate, Arctic Wolf's $3 million warranty cap works out to approximately £2.26 million ($3,000,000 divided by 1.3250).
Arctic Wolf and Sophos will not give you a number until you talk to sales. Arctic Wolf's MDR page offers only a demo request, and Sophos's own Get Pricing page states plainly that its "simple per-user and per-server pricing" is available only through a no-obligation quote from a sales representative. Unió Digital, a reseller that publishes a quarterly MDR and EDR pricing index alongside its own managed cybersecurity services, records both as quote-only, adds that Huntress's published rate applies on a 12-month term with no setup fee, and notes that Arctic Wolf deals are typically sold on multi-year terms. Neither the Huntress term detail nor the Arctic Wolf contract length appears on the vendors' own public pages, so treat both as starting questions for your own quote rather than a fixed rule. For budgeting purposes, that means a mid-market business cannot build a like-for-like cost comparison from public information alone; you have to request quotes from all three against the same endpoint count, term length and included modules before you can compare totals.
What Happens When You Actually Have an Incident
This is where the three services diverge most, and it is the detail most worth pressing suppliers on before you sign anything.
Sophos's entry MDR tier gives you 24/7 monitoring, investigation and response actions such as host isolation, process termination and IP blocking, guided by a Service Level Target rather than a contractual promise: a 2-minute target to case creation and a 30-minute target to the first action, which applies to both Sophos tiers, as published in Sophos's own MDR documentation. Step up to MDR Plus and Sophos adds a dedicated Incident Response Lead, a full remote incident-response engagement covering triage, containment and post-incident recommendations, and on top of the Service Level Target, a formal contractual Service Level Agreement: Sophos commits to a "Time to Respond" within 60 minutes for 90% of its highest-severity cases each month, backed by a service credit (the lesser of 5% of the previous billing cycle's fees or $5,000 USD) if it misses that commitment in more than three months of a rolling year, according to Sophos's live service description. MDR Plus also carries a Breach Protection Warranty covering confirmed ransomware incidents: Sophos will reimburse pre-approved expenses up to $1,000 per breached endpoint or paid licence, capped at $1,000,000 in aggregate per year, with a further $100,000 sub-limit on any ransomware payment itself, and a minimum of $5,000 in anticipated expenses needed to open a claim, according to Sophos's published warranty terms. That warranty only pays out if your Threat Response Mode is set to "Authorize" or "Collaborate" with the authorise-fallback enabled (plain "Collaborate" or "Notify Only" void it), your Sophos Health Check score stays at 100, you patch critical vulnerabilities within 7 days of release, and you report a suspected breach within 24 hours and file a claim within 15 days.
Arctic Wolf takes a different approach to the same worry. Instead of tiering incident response by product level, it bundles a Security Operations Warranty of up to $3 million (USD) into its offering, intended to help cover ransomware or business email compromise recovery costs and to fund a cyber-insurance deductible, a much broader incident scope and a far larger cap than Sophos's ransomware-only, $1,000,000-a-year warranty. No comparable financial warranty appears on the Huntress pages reviewed for this article; its incident-side commitment is the automated Managed Response feature described above, plus custom incident reporting included at no extra cost across its EDR tier. That is a genuinely different kind of support to a warranty payout or a named human Incident Response Lead, so a mid-market business should not assume Huntress's lower headline price buys the same depth of post-incident support as Sophos MDR Plus or Arctic Wolf's Concierge model.
Contract Terms, UK Presence and Getting a Quote
A UK mid-market IT security manager buying any of these three is not just buying software. All three now have UK-registered companies you can contract with locally: Sophos Limited is headquartered in Abingdon, Oxfordshire, Arctic Wolf Networks UK Ltd is based in Newcastle upon Tyne, and Huntress Labs UK Ltd is registered in London, all three showing as active companies on the UK's Companies House register. Huntress remains channel-first by design, though; it says most customers buy through a managed service provider or reseller, so day-to-day delivery for most UK buyers is still likely to run through a partner rather than direct with the vendor, even with a UK entity now in place.
That structure changes what a quote actually looks like. A UK-registered supplier such as Sophos, Arctic Wolf's UK entity, or Huntress's own UK entity can in principle issue a UK VAT invoice directly. Buying Huntress through a UK-based MSP instead, which Huntress itself recommends, means the MSP's own VAT registration, not the vendor's US pricing page, determines what you are charged and how VAT is handled, and it also means the MSP, not Huntress, typically owns day-to-day console management, alerting and escalation on top of the underlying SOC service. None of the published prices reviewed for this article are quoted in GBP, so ask every supplier for a sterling figure with the VAT treatment stated in writing before you compare totals against a budget. Our earlier piece on small UK resellers pairing Huntress with SentinelOne looks at the same channel from the partner's side, if you are weighing whether to build that capability rather than buy it as an end user.
Vendor and Option Comparison
| Criterion | Huntress Managed EDR | Arctic Wolf Aurora MDR | Sophos MDR (entry) | Sophos MDR Plus |
|---|---|---|---|---|
| Published price | $7.99 to $8.99 per endpoint/month | Quote-only | Quote-only | Quote-only |
| 24/7 human SOC | Included | Included (Concierge) | Included | Included |
| Automatic response option | Managed Response, on by default for new partners | Agentic SOC with human-in-the-loop response | "Authorize" mode | "Authorize" mode |
| Dedicated Incident Response Lead | Not published | Concierge security team per customer; not described as an IR lead role | Not included | Included |
| Contractual response-time SLA | Not published | Not published on reviewed pages | Service Level Target only, not contractual | Contractual SLA (60 minutes for 90% of top-severity cases) |
| Financial breach warranty | None found on reviewed pages | Up to $3 million (USD), per subscriber terms | None (tier not eligible) | Ransomware only: up to $1,000/endpoint, $1,000,000/year aggregate, $100,000 ransomware sub-cap |
| UK legal entity confirmed on Companies House | Yes, Huntress Labs UK Ltd, London (most sales still via MSP/reseller) | Yes, Arctic Wolf Networks UK Ltd, Newcastle | Yes, Sophos Limited, Abingdon | Yes, Sophos Limited, Abingdon |
| Typical contract term | 12 months per third-party research (see pricing section); not stated by Huntress itself | Often multi-year per third-party research (see pricing section); not stated by Arctic Wolf itself | Not published | Not published |
No single column wins outright. Huntress is the only one with a public price and a fast automated response by default; Sophos MDR Plus is the only one whose published terms name a dedicated Incident Response Lead and a contractual SLA; Arctic Wolf is the only one with a published, specific financial warranty figure, and a far higher one than Sophos's ransomware-only cap. Which row matters most depends on whether your priority is budget certainty, contractual accountability, or downside protection.
Our Editorial View for a Team Without a Dedicated SOC
Editorial analysis. For a UK mid-market business with a small IT team and no SOC, the choice comes down to how much you want decided for you versus how much you want to see in writing before you sign. Huntress gives you the clearest budget number and an automated response layer that acts fast, which suits a lean team that mainly wants alerts handled quickly and does not expect to negotiate contract terms heavily. Sophos MDR Plus suits a business that wants a published Incident Response Lead named in the service terms and a contractual response-time promise, but that depth is not available on the cheaper entry Sophos MDR tier, so check which one is actually being quoted. Arctic Wolf's Concierge model and its $3 million warranty suit a business more worried about the financial fallout of a bad incident than the mechanics of who clicks the isolate button, provided the multi-year commitment that third-party research associates with its deals fits your procurement appetite. None of these is a universal best choice; the right one depends on whether your priority is price certainty, contractual response guarantees, or financial downside protection.
Sources
- Huntress, Request Pricing for Managed EDR, ITDR, SAT, SIEM
- Huntress support, Managed Response, Automated Remediation of Incident Reports
- Arctic Wolf, Managed Detection and Response (MDR)
- Arctic Wolf, Security Operations Warranty
- Companies House, Arctic Wolf Networks UK Ltd
- Sophos, MDR Service Tiers documentation
- Sophos, MDR and MDR Plus Service Description
- Sophos, Get Pricing for Managed Detection and Response
- Companies House, Sophos Limited
- Sophos, Breach Protection Warranty terms
- Unió Digital, MDR and EDR Pricing Index
- Compare the Cloud, How Small UK Resellers Can Offer Managed Security Without Building a SOC
- FXStreet, British Pound softens to near 1.3250 as elevated US yields outweigh BoE's hawkish tone
- Companies House, Huntress Labs UK Ltd